


Latest Mar 16, 2026 Real FCSS_NST_SE-7.4 Exam Dumps Questions Valid FCSS_NST_SE-7.4 Dumps PDF
Fortinet FCSS_NST_SE-7.4 Exam Dumps - PDF Questions and Testing Engine
Fortinet FCSS_NST_SE-7.4 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 14
Which exchanges are the first two exchanges in IKEv2 negotiation?
- A. IKE SA_INIT and IKE_Auth
- B. INIT_Req and Auth_Request
- C. Key Exchange and Authentication
- D. Init_Req and Wait_Init_Req
Answer: A
Explanation:
The first IKEv2 exchange is the SA_INIT, where algorithms, nonces, and Diffie Hellman values are negotiated. The second is the AUTH exchange, which carries peer authentication and completes the IKE SA setup.
NEW QUESTION # 15
Exhibit.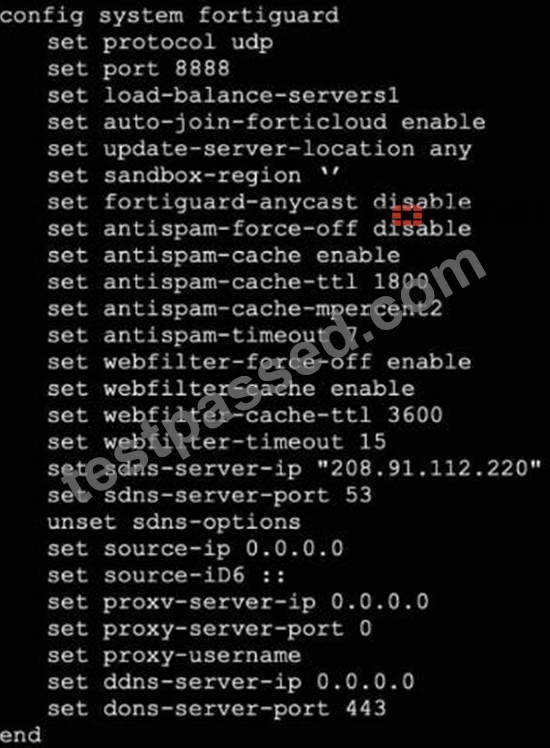
Refer to the exhibit, which shows a FortiGate configuration.
An administrator is troubleshooting a web filter issue on FortiGate. The administrator has configured a web filter profile and applied it to a policy; however the web filter is not inspecting any traffic that is passing through the policy.
What must the administrator do to fix the issue?
- A. Enable fortiguard-anycast.
- B. Increase webfilter-timeout.
- C. Change protocol to TCP.
- D. Disable webfilter-force-off.
Answer: D
NEW QUESTION # 16
Refer to the exhibit, which shows a truncated output of a real-time LDAP debug.
What two conclusions can you draw from the output? (Choose two.)
- A. FortiOS is able to locate the user in step 3 (Bind Request) of the LDAP authentication process.
- B. The user is authenticating using CN=John Smith.
- C. FortiOS is performing the second step (Search Request) in the LDAP authentication process.
- D. The name of the configured LDAP server is Lab.
Answer: B,C
NEW QUESTION # 17
Exhibit.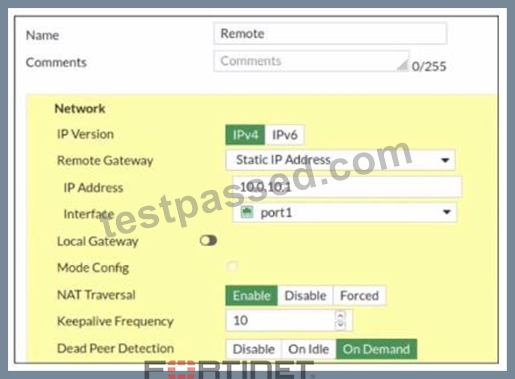
Refer to the exhibit, which contains a screenshot of some phase 1 settings.
The VPN is not up. To diagnose the issue, the administrator enters the following CLI commands on an SSH session on FortiGate: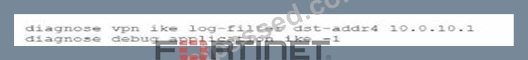
However, the IKE real-time debug does not show any output. Why?
- A. The administrator must also run the command diagnose debug enable.
- B. The log-filter setting is incorrect. The VPN traffic does not match this filter.
- C. Replace diagnose debug application ike -1 with diagnose debug application ipsec -1.
- D. The debug shows only error messages. If there is no output, then the phase 1 and phase 2 configurations match.
Answer: A
NEW QUESTION # 18
Refer to the exhibit, which shows the port1 interface configuration on FortiGate and partial session information for ICMP traffic.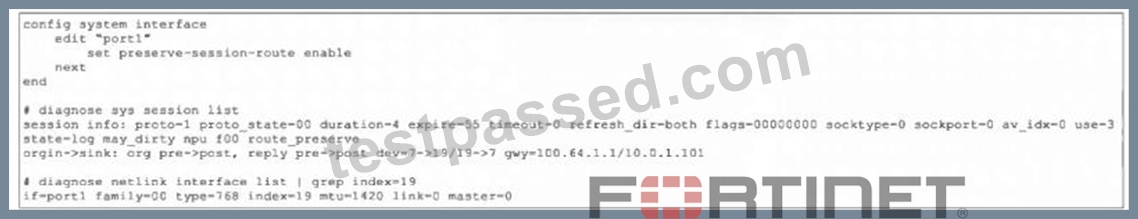
What happens to the session information if a routing change occurs that affects this session?
- A. Sessions involving port7 or port19 will not have their routing information flushed.
- B. Only the interface and gateway information for dev=7 will be removed.
- C. The session will be flagged as dirty but no route lookups will be performed.
- D. The session information will not change unless the current route has been removed from the routing table.
Answer: D
NEW QUESTION # 19
Refer to the exhibits.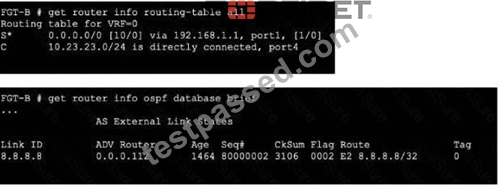
An administrator Is expecting to receive advertised route 8.8.8.8/32 from FGT-A. On FGT-B, they confirm that the route is being advertised and received, however, the route is not being injected into the routing table.
What is the most likely cause of this issue?
- A. FGT-B is configured with a prefix list denying the 8.8.8.8/32 network to be injected into the routing table.
- B. FGT-8 is configured with a distribution list denying the 8.8.8.8/32 network to be injected into the routing table.
- C. A batter route to the 8.8.8.8/32 network exists in the routing table.
- D. The administrator has misconfigured redistribution of routes on FGT-A.
Answer: A
NEW QUESTION # 20
Refer to the exhibit, which shows the output of a session. Which two statements are true?
(Choose two.)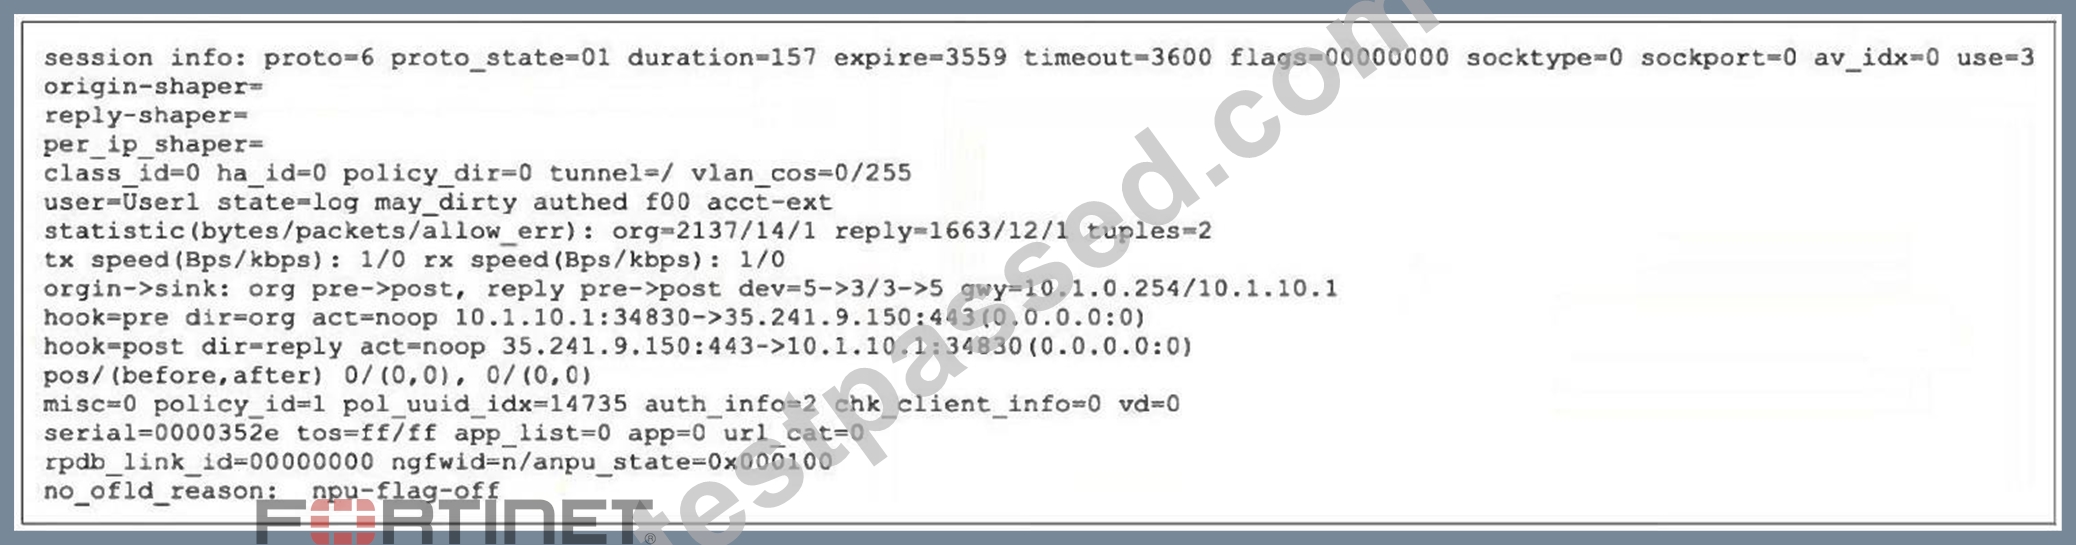
- A. The session is being offloaded.
- B. The TCP session has been successfully established.
- C. The session is being inspected using flow inspection.
- D. The session was initiated from an authenticated user.
Answer: B,D
Explanation:
The TCP session has been successfully established.
The proto=6(TCP) with proto_state=01and a non zero duration/expireindicates the three way handshake completed and the session is up.
The session was initiated from an authenticated user.
The line user=User1 state=log ... authedshows the session is tied to a logged in user (User1).
NEW QUESTION # 21
Refer to the exhibit, which shows the output of a policy route table entry.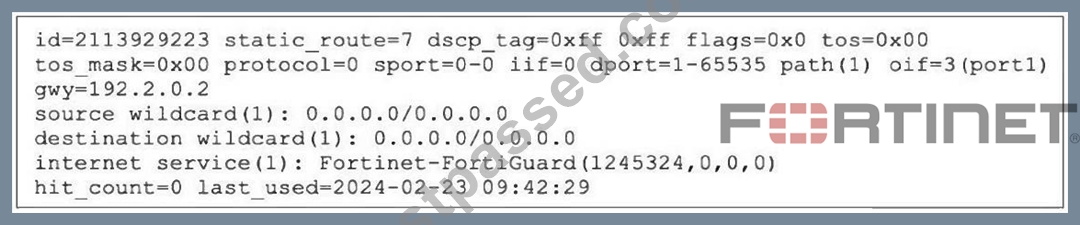
Which type of policy route does the output show?
- A. A regular policy route
- B. An SD-WAN rule
- C. A regular policy route, which is associated with an active static route in the FIB
- D. An ISDB route
Answer: D
Explanation:
From the reference to the "internet service(1): Fortinet-FortiGuard(...)" object in the output, it is clear that this policy route entry is using an Internet Service Database (ISDB) object rather than a conventional address object.
NEW QUESTION # 22
Refer to the exhibit, which shows the partial output of a real-time OSPF debug.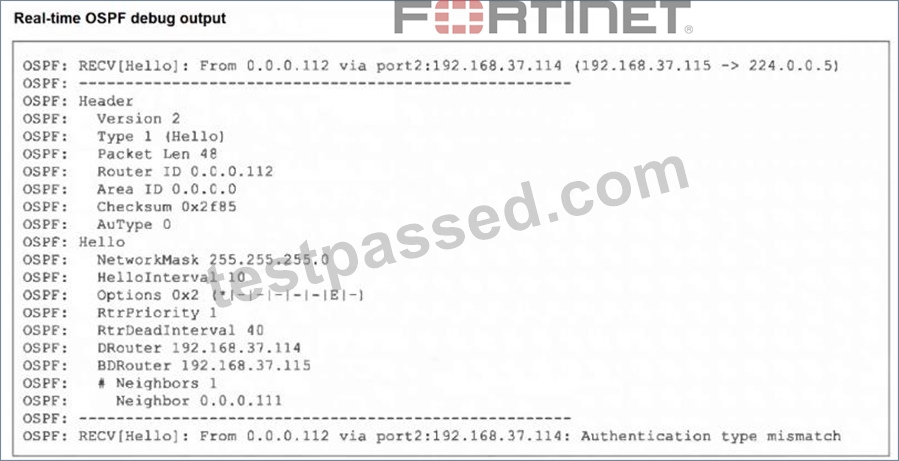
Why are the two FortiGate devices unable to form an adjacency?
- A. The passwords on the FortiGate devices do not match.
- B. The two FortiGate devices attempting adjacency are in area 0.0.0.0.
- C. The Hello packet is being sent from an OSPF router with ID 0.0.0.112.
- D. One FortiGate device is configured to require authentication, while the other is not.
Answer: D
NEW QUESTION # 23
Refer to the exhibit showing a debug output.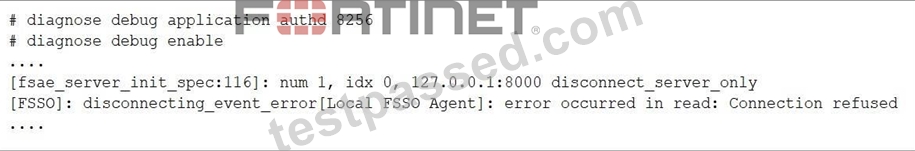
An administrator deployed FSSO in DC Agent Mode but FSSO is failing on FortiGate. Pinging FortiGate from where the collector agent is deployed is successful. The administrator then produces the debug output shown in the exhibit.
What could be causing this error message?
- A. The FortiGate cannot resolve the active directory server name.
- B. The FortiGate and the collector agent are using different TCP ports.
- C. The collector agent preshared password is mismatched.
- D. The TCP port 445 is blocked between FortiGate and collector agent.
Answer: B
Explanation:
The log shows FortiGate attempting to connect to 127.0.0.1:8000 and immediately getting
"Connection refused," which means no process is listening on that port. In DC Agent mode both sides must match on the same TCP port (default 8000), so a port mismatch will cause exactly this error.
NEW QUESTION # 24
Refer to the exhibit, which shows a truncated output of a real-time LDAP debug.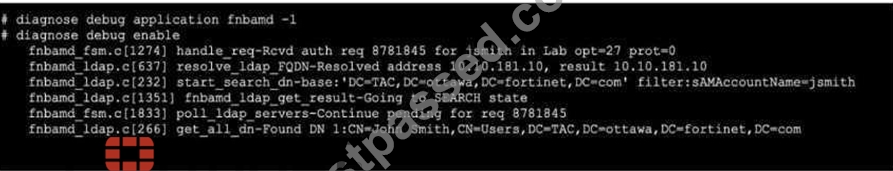
What two conclusions can you draw from the output? (Choose two.)
- A. FortiOS is able to locate the user in step 3 (Bind Request) of the LDAP authentication process.
- B. The user is authenticating using CN=John Smith.
- C. FortiOS is performing the second step (Search Request) in the LDAP authentication process.
- D. The name of the configured LDAP server is Lab.
Answer: B,C
NEW QUESTION # 25
Refer to the exhibit. The exhibit shows the output from using the command diagnose debug application samld -1 to diagnose a SAML connection.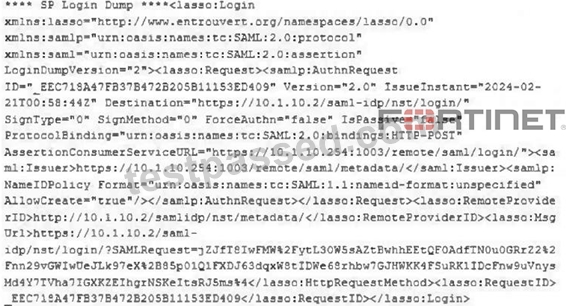
Based on this output, what can you conclude?
- A. The authentication request is for an SSL VPN connection.
- B. The IdP IP address is 10.1.10.2.
- C. Active Directory is used for authentication.
- D. The IdP IP address is 10.1.10.254.
Answer: B
Explanation:
The SAML AuthnRequest's Destination and RemoteProviderID URLs both point to https://10.1.10.2, indicating the IdP's IP address is 10.1.10.2.
NEW QUESTION # 26
Refer to the exhibit, which shows a session entry.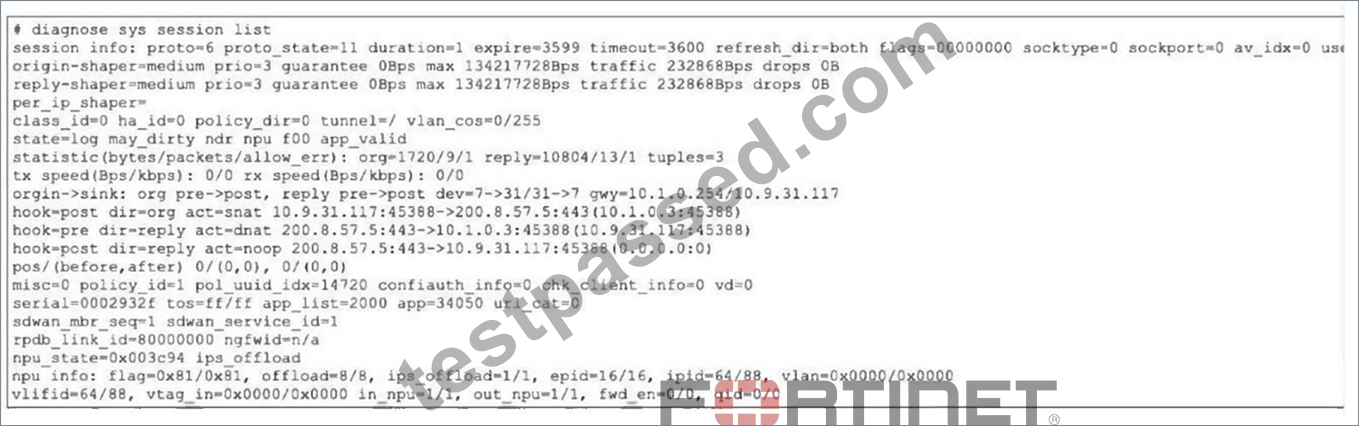
Which statement about this session is true?
- A. Return traffic to the initiator is sent lo 10.200.1.254.
- B. Return traffic to the initiator is sent to 10.1.0.1.
- C. It is an ICMP session from 10.1.10.1 to 10.200.5.1.
- D. It is an ICMP session from 10.1.10.10 to 10.200.1.1.
Answer: B
Explanation:
Return packet routing back to the source follows this format gwy=10.200.1.254 (this is the gateway to the dest) / 10.1.0.1 (this is the destination's gateway back to the source).
NEW QUESTION # 27
Refer to the exhibit, which shows a partial output of the fssod daemon real-time debug command.
What two conclusions can you draw Itom the output? (Choose two.)
- A. FSSO is using agentless polling mode to detect logon events.
- B. FSSO is using DC agent mode to detect logon events.
- C. The workstation with IP 10.124.2.90 will be polled frequently using TCP port 445 to see if the user is still logged on.
- D. The logon event can be seen on the collector agent installed on Windows.
Answer: A,C
NEW QUESTION # 28
Exhibit.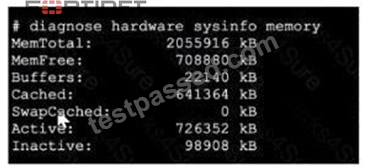
Refer to the exhibit, which shows a partial output of diagnose hardware aysinfo memory.
Which two statements about the output are true? (Choose two.)
- A. The value indicated next to the inactive heading represents the currently unused cache page.
- B. The I/O cache, which has 641364 kB of memory allocated to it.
- C. The user space has 708880 kB of physical memory that is not used by the system.
- D. There are 98908 kB o! memory that will never be used.
Answer: A,D
NEW QUESTION # 29
Which three steps does FortiGate execute using the pull method to get antivirus and IPS updates? (Choose three.)
- A. FortiGate gets a list of server IP addresses that it can contact.
- B. FortiGate registers its public IP address in FortiGuard.
- C. FortiGate contacts a DNS server to resolve the FortiGuard domain name.
- D. FortiGate starts sending rating queries to one of the servers in the list.
- E. FortiGate periodically queries for pending updates.
Answer: A,C,E
NEW QUESTION # 30
Refer to the exhibit, which shows partial outputs from two routing debug commands.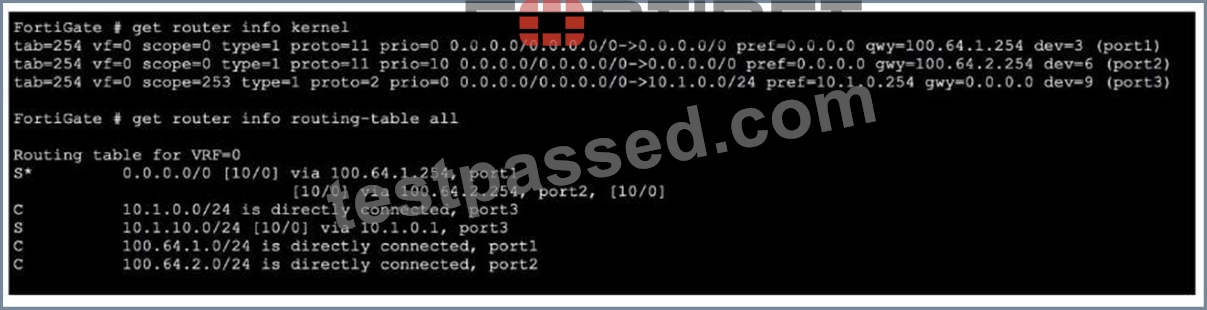
Which change must an administrator make on FortiGate to route web traffic from internal users to the internet, using ECMP?
- A. Set preserve-session-route to enable.
- B. Set the priority of the static default route using port2 to 1.
- C. Set the priority of the static default route using port1 to 10.
- D. Set snat-route-change to enable.
Answer: C
NEW QUESTION # 31
Refer to the exhibit, which shows the output of a debug command.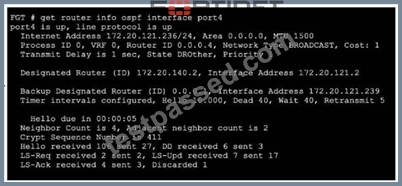
Which two statements about the output are true? (Choose two.)
- A. The interlace is part of the OSPF backbone area.
- B. One of the neighbors has a router ID of 0.0.0.4.
- C. In the network connected to port4, two OSPF routers are down.
- D. There are a total of five OSPF routers attached to the vorz4 network segment
Answer: A,C
NEW QUESTION # 32
Consider the scenario where the server name indication (SNI) does not match either the common name (CN) or any of the subject alternative names (SAN) in the server certificate. Which action will FortiGate take when using the default settings for SSL certificate inspection?
- A. FortiGate uses the CNinformation from the Subjectfield in the server certificate.
- B. FortiGate closes the connection because this represents an invalid SSL/TLS configuration.
- C. FortiGate uses the SNI from the user's web browser.
- D. FortiGate uses the first entry listed in the SAN field in the server certificate.
Answer: A
Explanation:
#Config firewall ssl-ssh-profile
edit <profile_name>
config https
set sni-server-cert-check [enable* | strict | disable]
Enable: If the SNI does NOT match the CN or SAN fields in the returned server's certificate, FG uses the CN field instead of the SNI to obtain the FQDN.
Strict: If the SNI does NOT match the CN or SAN fields in the returned server's certificate, FG closes the connection.
Disable: FG does not check the SNI.
NEW QUESTION # 33
Refer to the exhibit, which shows the partial output of diagnose sys session stat.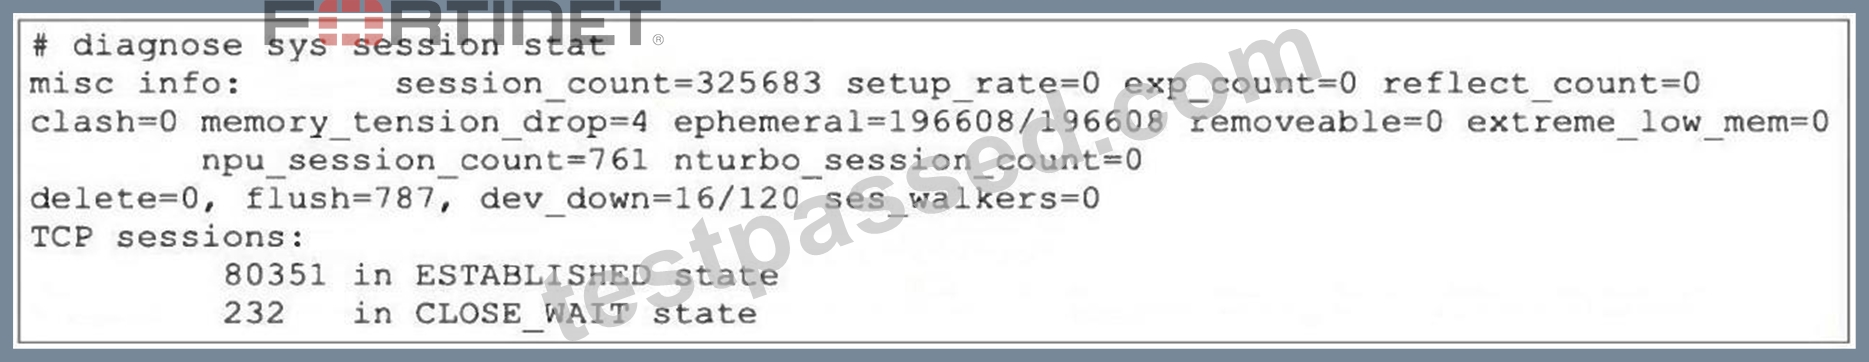
An administrator has noticed unusual behavior from FortiGate. It appears that sessions are randomly removed.
Which two reasons could explain this? (Choose two.)
- A. The FortiGate is flushing sessions because of high memory usage.
- B. The FortiGate is not accepting sessions because the device has been down 16 out of 120 seconds.
- C. The FortiGate is deleting sessions because the kernel cannot allocate more memory pages.
- D. The FortiGate is dropping all TCP sessions with incomplete three-way handshakes.
Answer: B,C
Explanation:
The FortiGate is deleting sessions because the kernel cannot allocate more memory pages.
The memory_tension_drop=4counter shows that, under memory pressure, the oldest sessions are being removed when the system can't allocate new session blocks The FortiGate is not accepting sessions because the device has been down 16 out of 120 seconds.
The dev_down=16/120counter indicates 16 sessions were deleted due to an interface going down within the last 120 seconds
NEW QUESTION # 34
Which command do you use to enable a timestamp in a real-time debug?
- A. diagnose timestamp enable
- B. diagnose application timestamp enable
- C. diagnose debug console timestamp enable
- D. diagnose debug application timestamp enable
Answer: C
NEW QUESTION # 35
Exhibit.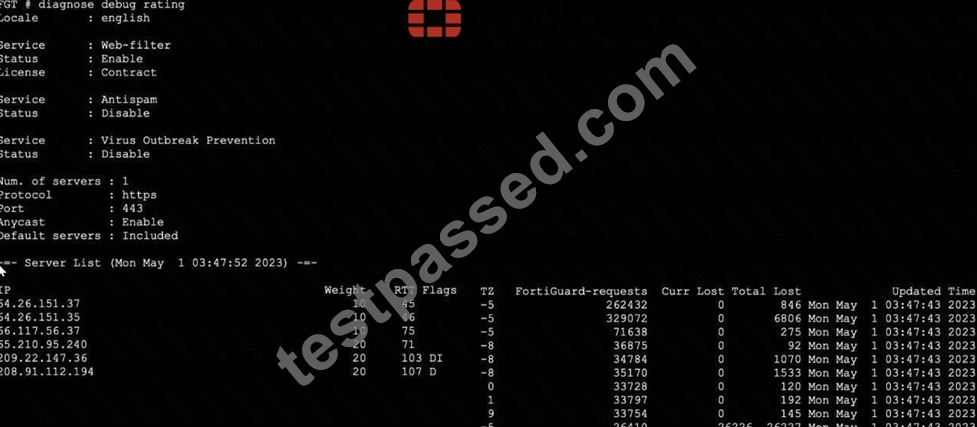
Refer to the exhibit, which shows the output of a diagnose command.
What can you conclude about the debug output in this scenario?
- A. Servers with a negative TZ value are less preferred for rating requests.
- B. There is a natural correlation between the value in the FortiGuard-requests field and the value in the Weight field.
- C. FortiGate used 64.26.151.37 as the initial server to validate its contract.
- D. The first server provided to FortiGate when it performed a DNS query looking for a list of rating servers, was 121.111.236.179.
Answer: B
NEW QUESTION # 36
......
Reliable Fortinet Certified Solution Specialist FCSS_NST_SE-7.4 Dumps PDF Mar 16, 2026 Recently Updated Questions: https://www.testpassed.com/FCSS_NST_SE-7.4-still-valid-exam.html
Latest FCSS_NST_SE-7.4 Exam Dumps for Pass Guaranteed: https://drive.google.com/open?id=1ajsSGgrogHBocmf8MLB3JjZhyCwMEcSV